OSINT Walkthrough: "Never Deleted" (OSINT Industries) – Tracking a Threat Actor via Malware Sandboxes
Bu çözümün Türkçesi de var: sağ üstten dili TR yapın.
Challenge Overview
In this OSINT Industries challenge titled “Never Deleted”, the objective was to trace the digital footprint of a known threat actor operating under the handle Mrb3hz4d. According to the scenario, investigators identified the suspect as a fan of rap music who published a short rap clip on August 22, 2019. The mission was to track down this post using passive OSINT methodologies and determine the full name of the featured artist.
- Platform: OSINT Industries
- Challenge Name: Never Deleted
- Target Handle:
Mrb3hz4d - Target Post Date: August 22, 2019
- Objective: Locate the post and identify the full name of the featured rapper.
Step 1: Handle Reconnaissance & Threat Profile
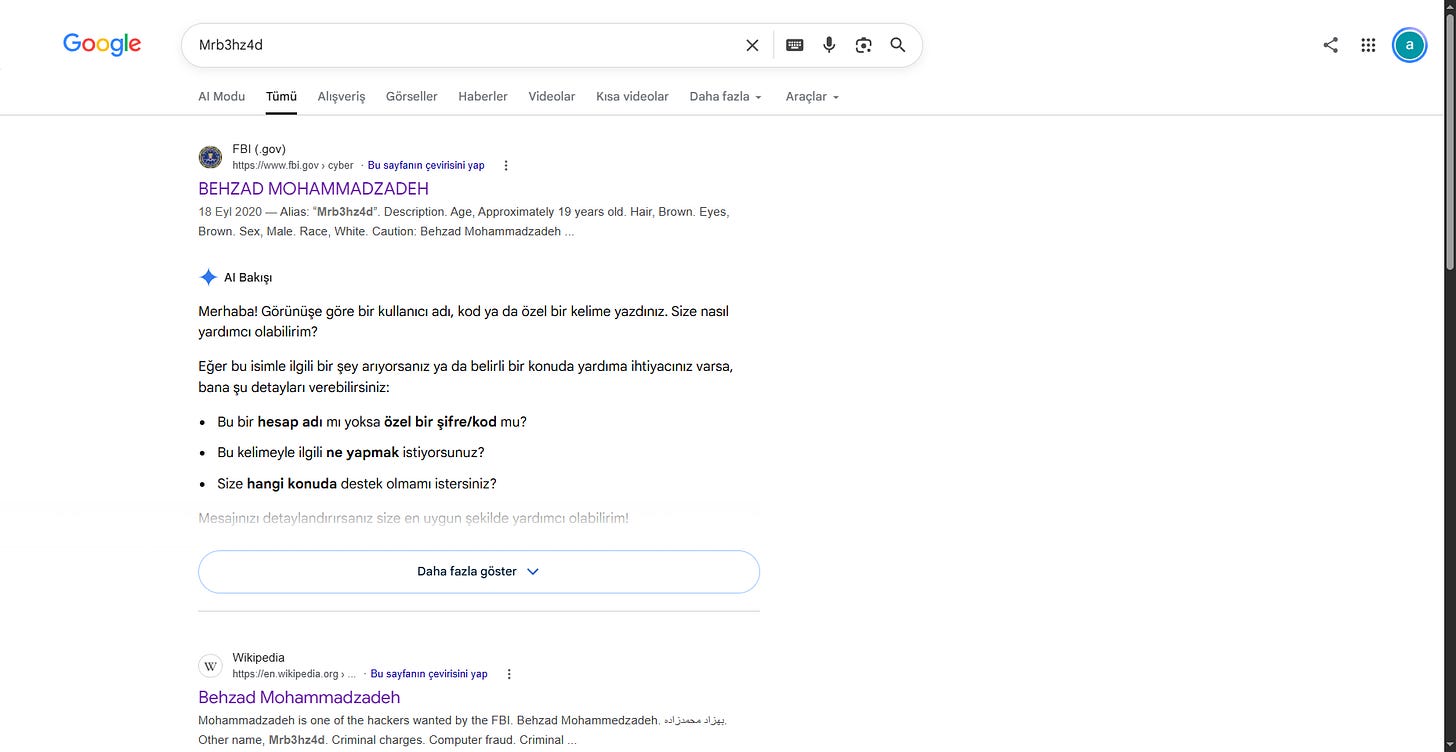
The investigation started with an open query for the handle Mrb3hz4d. The initial results pointed directly to law enforcement alerts, specifically an FBI wanted notice and a Wikipedia entry identifying the suspect behind the alias as Behzad Mohammadzadeh.
Step 2: Reviewing the Legal Indictment
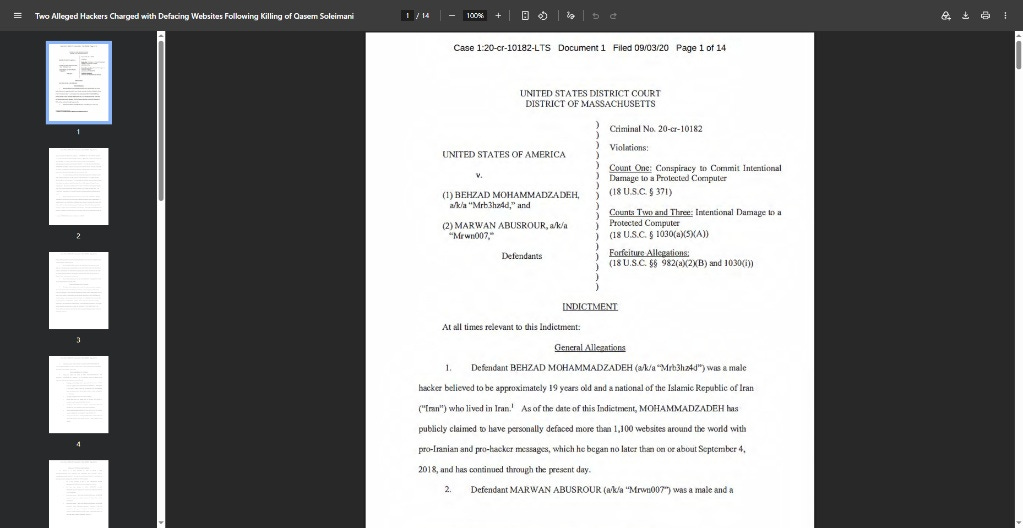
Following the trail of formal records, I pulled the official indictment released by the U.S. Department of Justice (1:20-cr-10182-LTS). The filing outlined his cyber activities, unauthorized access offenses, and defacement operations. While it confirmed his operational identity, the indictment did not directly reference specific active social accounts or the 2019 clip in question.
Step 3: Uncovering Defacement Footprints & Social Handles
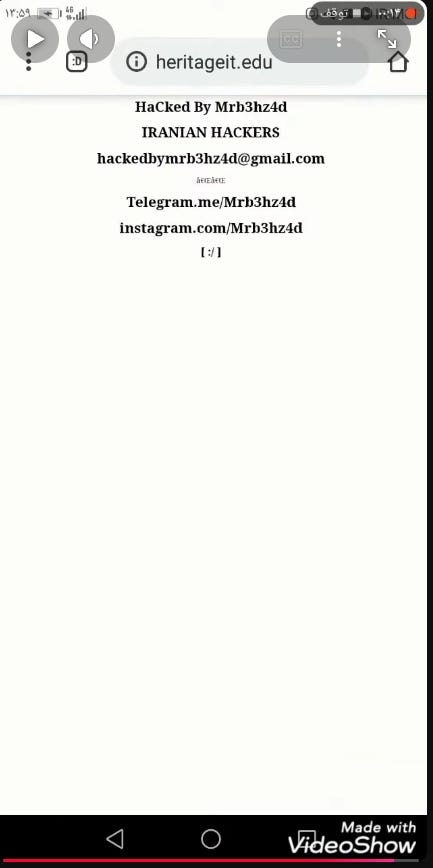
To locate live or past handles, I inspected defacement logs associated with the actor. One recorded target (heritageit.edu) displayed an Iranian defacement splash screen, openly listing his contact vectors: an email address, a Telegram channel, and an Instagram account ([instagram.com/Mrb3hz4d](https://instagram.com/Mrb3hz4d)). Although this confirmed his platform presence, the defacement timestamp did not match the required target date of August 22, 2019
.
Step 4: The Pivot – “Never Deleted” via ANY.RUN Sandbox
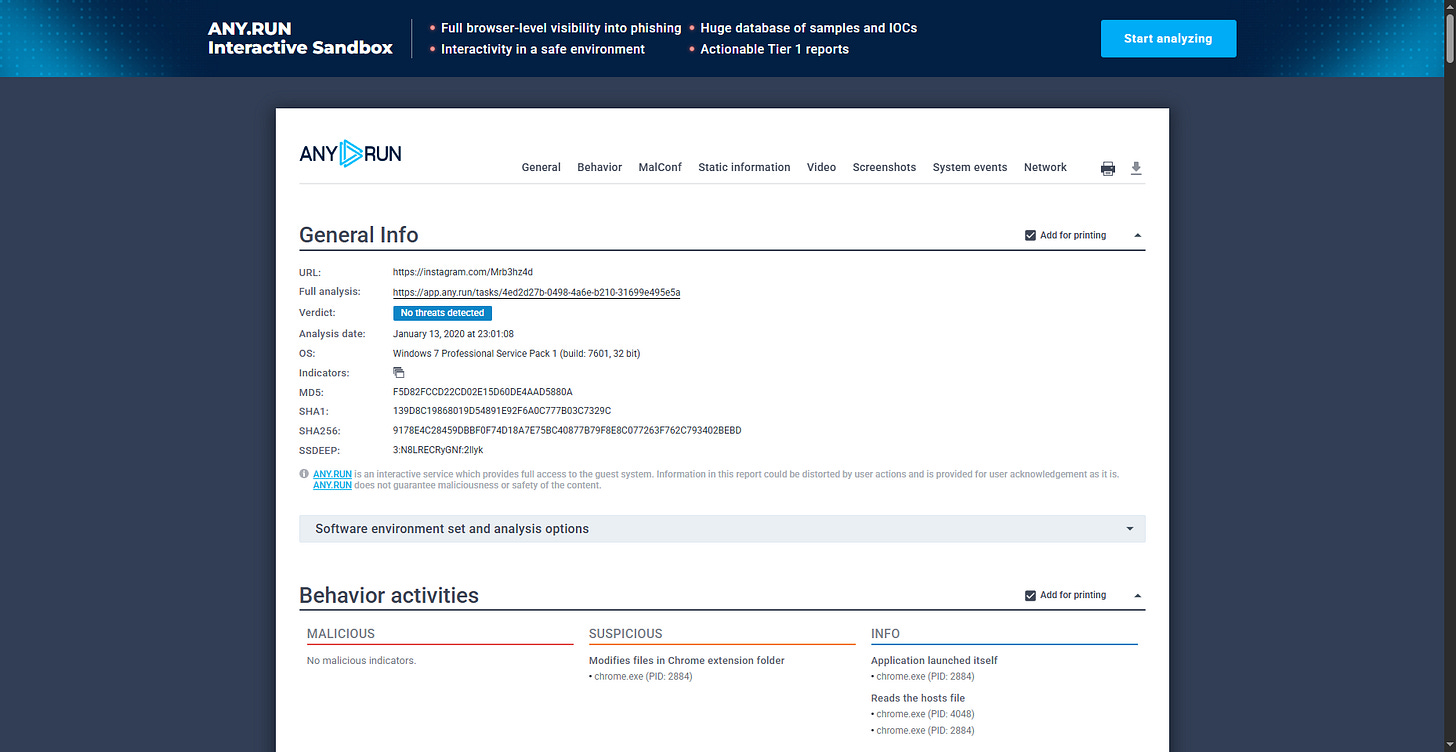
Standard search engines and modern social platform caches often fail to preserve deleted posts from sanctioned or banned accounts. Living up to the challenge’s title—Never Deleted—I pivoted to dynamic malware and threat intelligence sandboxes to look for automated web environment captures.
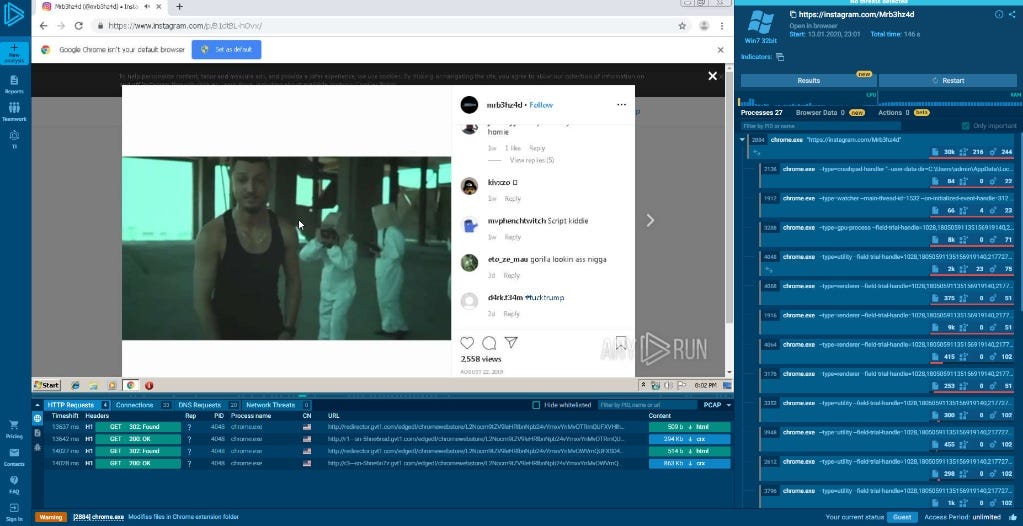
A targeted query on ANY.RUN surfaced an interactive analysis session from January 13, 2020, where an analyst executed and captured [https://instagram.com/Mrb3hz4d](https://instagram.com/Mrb3hz4d)
Step 5: Pinpointing the Target Media & Timestamp
Navigating through the virtual desktop session of the sandbox, I was able to interact with the profile as it appeared in early 2020. Browsing backwards through the timeline, I located a video post showing an artist performing in an industrial building alongside masked individuals. Examining the post details confirmed the publication date: August 22, 2019.
Step 6: Reverse Image Search & Artist Identification
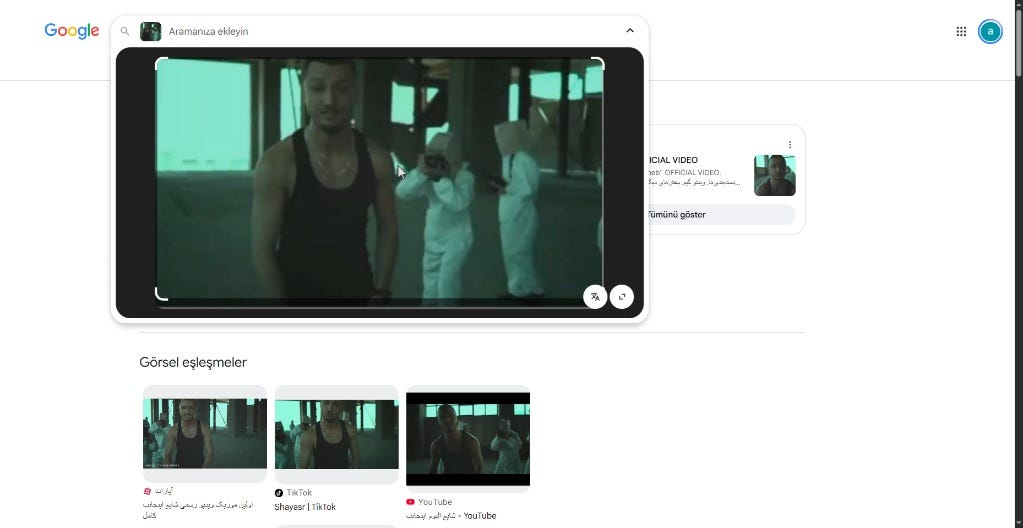
Having captured a clear frame showing the artist’s face, I submitted the crop to Google Lens. The visual signature produced immediate matches across Iranian multimedia platforms, Aparat, and YouTube, linking the footage to popular Iranian rapper Shayea.
Cross-referencing the stage alias with biographical records provided the requested full name: Mohammadreza Shayea.
Originally published on Substack